[ SECURITY_OPERATIONS / ENTRY_LEVEL ]

VEERAMALLU
VAMSI KRISHNA

Final-year CSE student pursuing cybersecurity through hands-on labs, TryHackMe training, and personal projects.

LOCATION
Hyderabad, India
FOCUS
SOC / Security Ops
TRAINING
Defensive Security/dd>
STATUS
Open to roles
01

WHOAMI

$ whoami
final-year computer science student building practical foundations in defensive security.

I’m Vamsi Krishna, a final-year Computer Science student in Hyderabad actively pursuing cybersecurity. I’m focused on SOC and security operations, using personal labs and projects to develop practical skills with Splunk, Sysmon, Kali Linux, and Windows / Active Directory fundamentals.

02

PROJECTS / CASE STUDIES

Personal projects and controlled simulations — presented with the evidence and scope available.

PROJECT_01 / PERSONAL_HOME_LAB

SIEM HOME LAB

VIEW ON GITHUB ↗

Built a SOC-style home lab simulating threat detection workflows using Splunk and Sysmon on a local virtual network.

WHAT I BUILT / INVESTIGATED

  • • Configured Active Directory with domain users and monitored authentication events via Windows Event Logs.
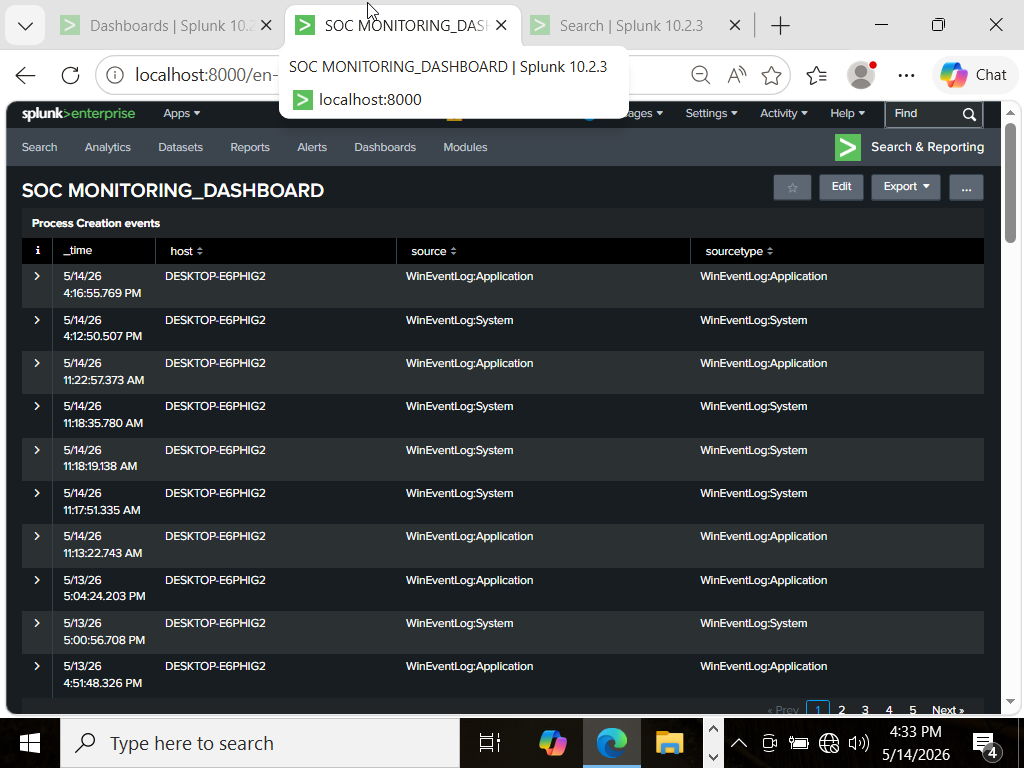
  • • Created Splunk dashboards and alerts for failed logins, process creation, and reconnaissance activity.
  • • Simulated basic attacker behavior with Kali Linux and Nmap.
  • • Mapped findings to the MITRE ATT&CK framework.

TECHNOLOGIES

Splunk · Sysmon · Active Directory · Kali Linux · VirtualBox

Open case study notes

OBJECTIVE
Simulate threat detection workflows in a SOC-style home lab.

ENVIRONMENT
Local virtual network using Windows Server, Active Directory, Kali Linux, and VirtualBox.

LOG SOURCES
Windows Event Logs and Sysmon.

DETECTION
Failed logins, process creation, and reconnaissance activity in Splunk.

INVESTIGATION
Investigated process creation, failed and successful logons, security events, and Nmap reconnaissance activity in Splunk.

MITRE ATT&CK
T1046 (Network Service Scanning), T1078 (Valid Accounts), and T1110 (Brute Force).

LESSONS LEARNED
Built practical experience collecting, investigating, and visualizing Windows security telemetry.

LAB FLOW
KALI LINUX
NMAP / BASIC ATTACKER ACTIVITY
WINDOWS SERVER + ACTIVE DIRECTORY
WINDOWS EVENT LOGS + SYSMON
SPLUNK
DASHBOARDS / ALERTS
DETECTION / INVESTIGATION
MITRE ATT&CK
Real Splunk SOC monitoring dashboard screenshot showing process creation events from the SIEM Home Lab
VISUAL EVIDENCE / Splunk SOC monitoring dashboard — process creation events

PROJECT_02 / CONTROLLED_SIMULATION

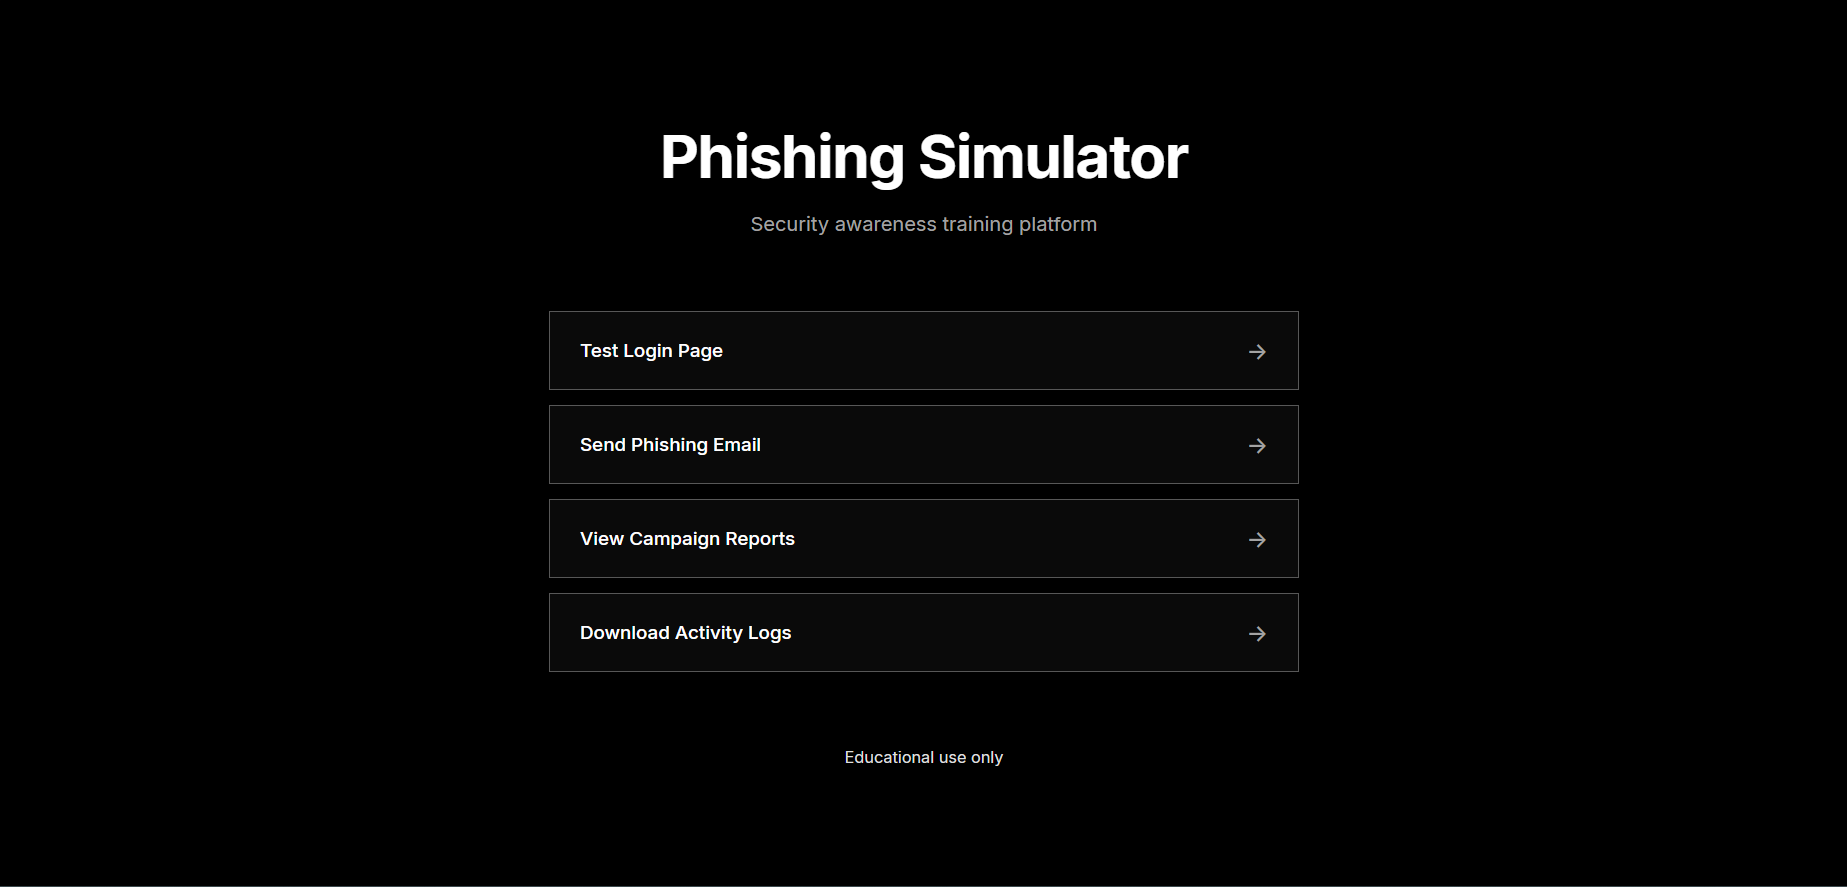
PHISHING SIMULATOR

VIEW ON GITHUB ↗

Built a phishing simulation tool with fake login pages, click-tracking, and a simple campaign dashboard.

WHAT I BUILT / IMPLEMENTED

  • • Implemented user authentication, session management, audit logging, and basic input validation.
  • • Designed an admin panel for viewing campaign results.
  • • Added basic risk scoring.

TECHNOLOGIES

Python (Flask) · JavaScript · SQLite · SMTP · HTML/CSS

Open case study notes

OBJECTIVE
Build a controlled phishing simulation tool.

ARCHITECTURE
Python and Flask platform with JavaScript, SQLite, and HTML/CSS.

SIMULATION FLOW
Fake login pages, user interaction, click-tracking, campaign dashboard, and basic risk scoring.

TECHNOLOGY
Python (Flask), JavaScript, SQLite, SMTP, and HTML/CSS.

TRACKING
Click-tracking.

AUDIT LOGGING
Implemented audit logging.

LESSONS LEARNED
Implemented authentication, session management, audit logging, activity tracking, and basic risk scoring.

SIMULATION FLOW

SIMULATION
FAKE LOGIN PAGE
USER INTERACTION
CLICK TRACKING
CAMPAIGN DASHBOARD
RISK SCORING
AUDIT LOGS
Real screenshot of the Phishing Simulator security awareness training platform
VISUAL EVIDENCE / Phishing Simulator interface
03

CERTIFICATIONS / ACHIEVEMENTS

ACHIEVEMENTS / PARTICIPATION

04

EXPERIENCE

ZARAVYA TECHNOLOGIES

Software Engineer Intern

May 2026 – Present

  • • Testing web application functionality across loyalty and HR platforms using Postman and Chrome DevTools.
  • • Analyzing API responses and identifying edge cases, inconsistent behavior, and input handling issues.
  • • Exploring security-relevant flows such as OTP handling and session behavior as part of personal learning.
  • • Documenting issues with reproduction steps, severity notes, and suggested fixes.
  • • Performing cross-browser and UI responsiveness testing on live applications.

EDUCATION

DRK Institute of Science & Technology

B.Tech, Computer Science & Engineering · 4th Year · Hyderabad

CGPA: 7.5

05

SECURITY TOOLKIT

CYBERSECURITY

Splunk · Sysmon · Active Directory Basics · MITRE ATT&CK · Threat Detection · Log Analysis · SOC Workflows · Phishing Simulation

TOOLS & OS

Kali Linux · Windows Server · Linux CLI · Postman · Chrome DevTools · VirtualBox · Git & GitHub · Wireshark (learning)

DEVELOPMENT

Python · Flask · JavaScript · HTML5 · CSS3 · SQL · SQLite

06

CONTACT

SECURE CHANNEL / LET'S CONNECT

veeramalluvamsi12345@gmail.com

Hyderabad, Telangana, India